Not shared SaaS
Run a dedicated Accepire AI Gateway instance in the Azure environment your organization controls.
- Customer-owned subscription
- Dedicated production instance
- Private networking support
- Customer-selected Azure regions
Platform
Detect Saudi identifiers, local number formats, credentials, and configured Arabic personal data before prompts reach your customer-owned Azure OpenAI or Microsoft Foundry models—then apply the same policy across chat, Teams, coding tools, and internal applications.
Run a dedicated Accepire AI Gateway instance in the Azure environment your organization controls.
Use your existing Microsoft identity lifecycle instead of creating another unmanaged directory.
Apply data-handling rules before content reaches a model and, where configured, before responses reach users.
Give each team the models and capacity it needs without applying one permissive policy to the whole organization.
Turn model activity into information that finance, IT, and business owners can act on.
Review policy decisions and export evidence without making raw prompts broadly visible.
Inside the protection workflow
These sample screens show how findings, redacted content, and reviewer activity appear in the gateway.
See detected categories alongside the original text and the redacted content sent to the model.
Open full-size image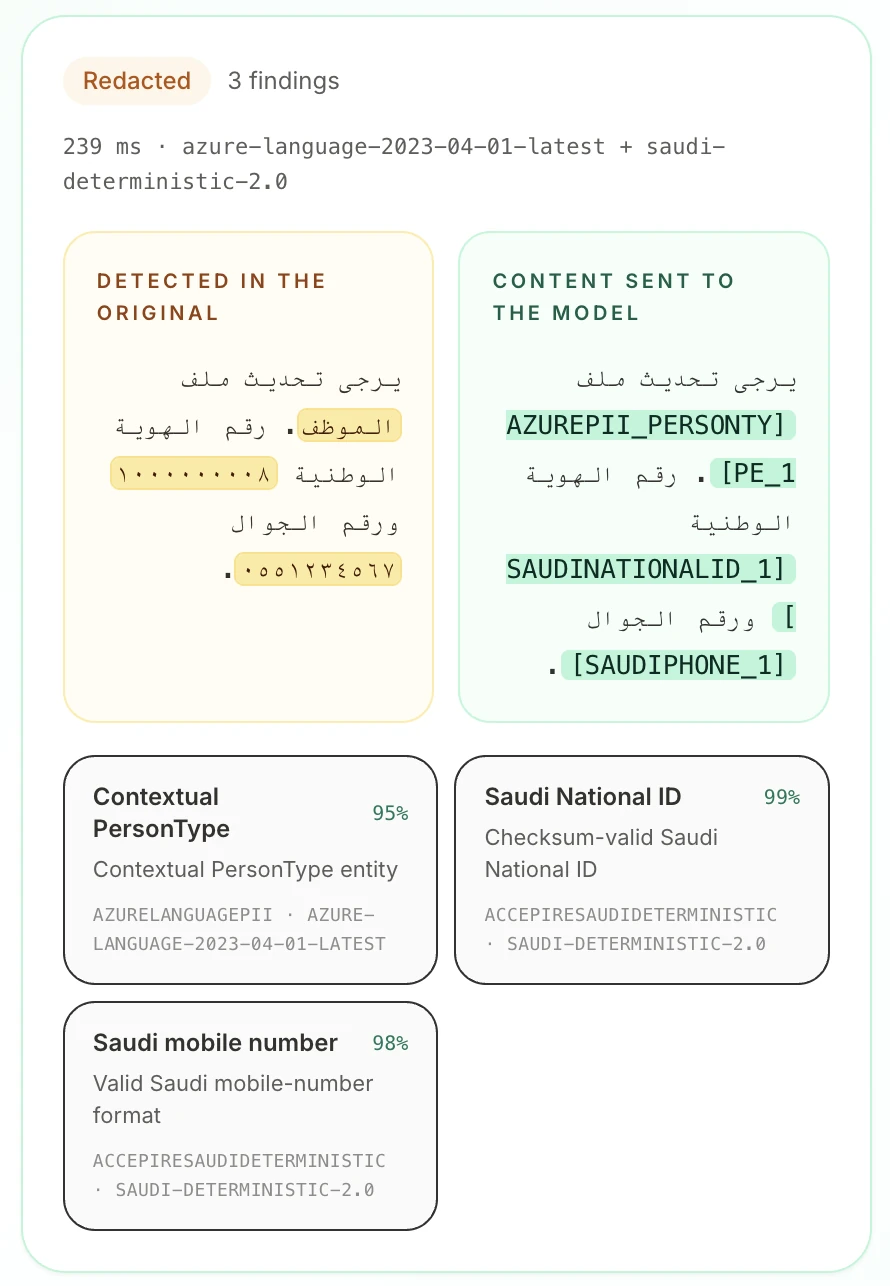
Authorized reviewers can inspect redacted request and response content. Access to the record is added to the administrative audit log.
Open full-size image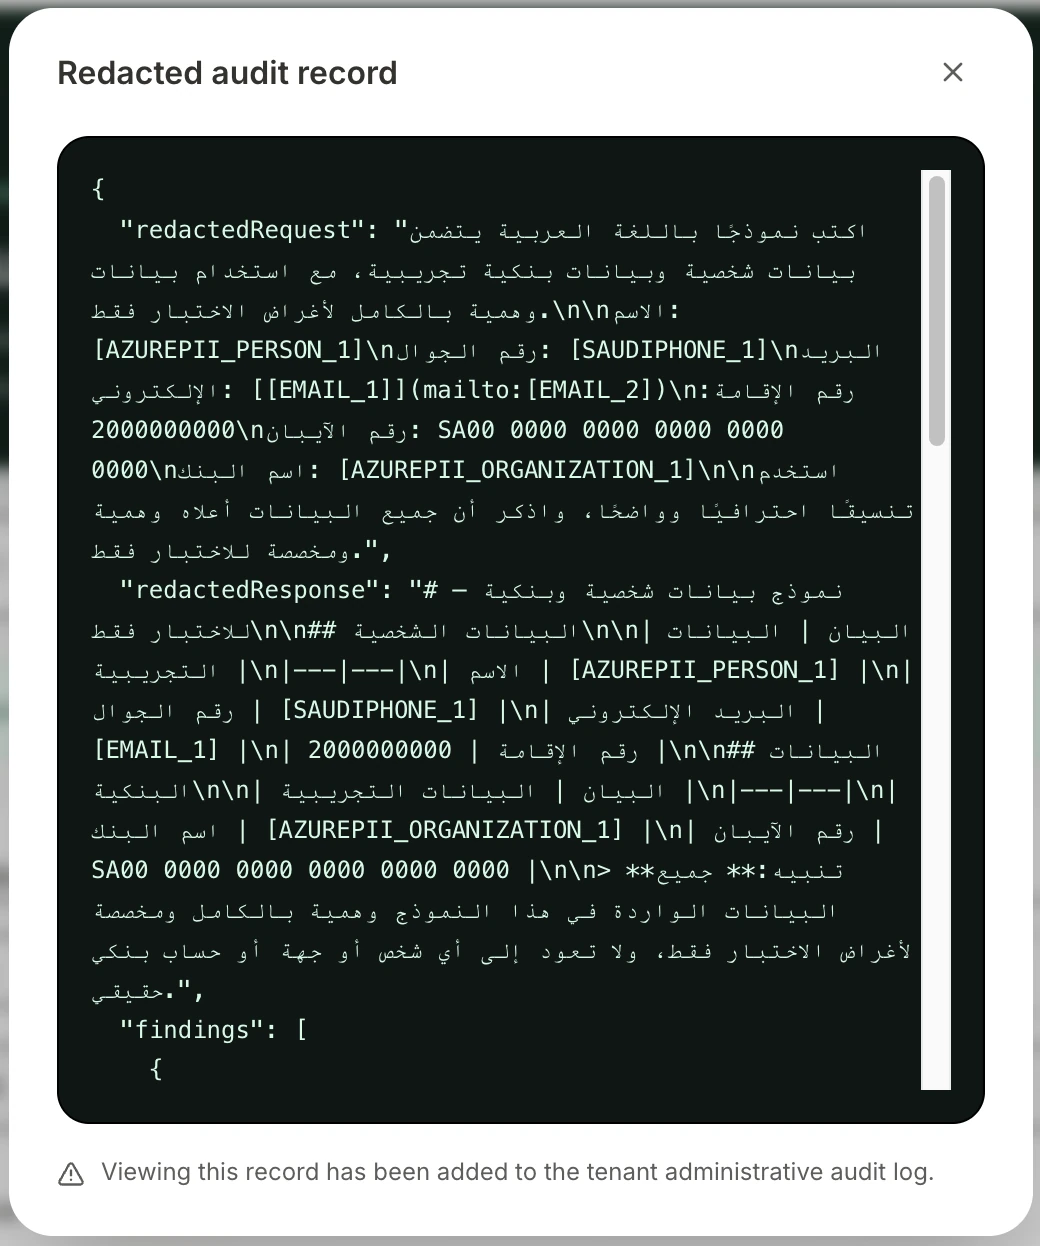
Policy in the request path
Users get a consistent experience. Administrators get one place to enforce policy, regardless of the channel that generated the request.
Accepire AI Gateway identifies the person, application, workspace, and department.
Access, model, budget, residency, and sensitive-data policies are checked.
Approved requests are sent to an authorized Azure OpenAI or Foundry deployment.
Usage, cost estimates, and policy outcomes become governed evidence.
Data protection
The gateway normalizes Western, Arabic-Indic, and Eastern Arabic digits, validates structured Saudi identifiers, and checks context where a number alone is not enough. Configure an action by category, test it without adding the sample to the prompt audit, and let authorized reviewers see privacy-safe evidence.
DLP reduces risk but does not replace classification, access governance, employee training, or legal review.
Saudi formats
Checksum-validated National IDs and Iqamas, MOD-97-validated IBANs, and Saudi mobile formats
Context-aware records
Label-aware commercial registrations and validated Hijri dates with relevant surrounding context
Credentials and secrets
API keys, private keys, bearer tokens, JWTs, and connection strings
Arabic personal data
Configured Arabic and English entity detection through the customer's Azure AI Language resource
Organization-specific data
Custom patterns for internal identifiers and sensitive formats
Access channels
A familiar AI experience backed by organization policy.
Bring approved models into a collaboration tool employees already use.
Connect compatible coding agents without distributing provider credentials.
Use OpenAI-compatible endpoints for controlled application access.
Connect your Azure OpenAI or Microsoft Foundry deployments with an API key or managed identity. Accepire AI Gateway does not resell model tokens.
Set audit modes and retention periods according to your risk and operational requirements.
Assign administrators, reviewers, departments, and access rules that reflect how your organization works.
We’ll walk through deployment boundaries, identity, model connectivity, data handling, governance, and a practical pilot scope.
Request a demo