01
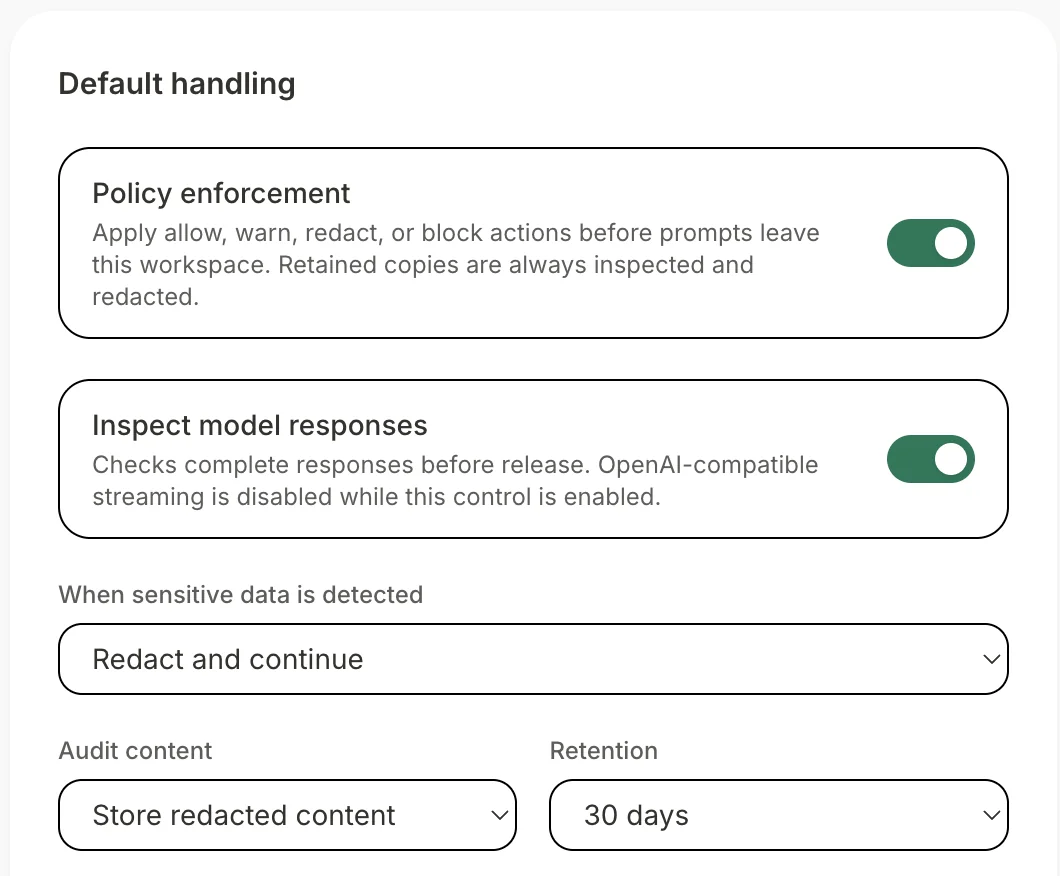
Choose the action
Apply a default response and retain only the evidence your policy permits.
The Accepire Saudi Data Protection Engine
Give your teams governed access to Azure AI, with Saudi identifier checks, access policies, and audit records in your Azure environment.
View the pilot brief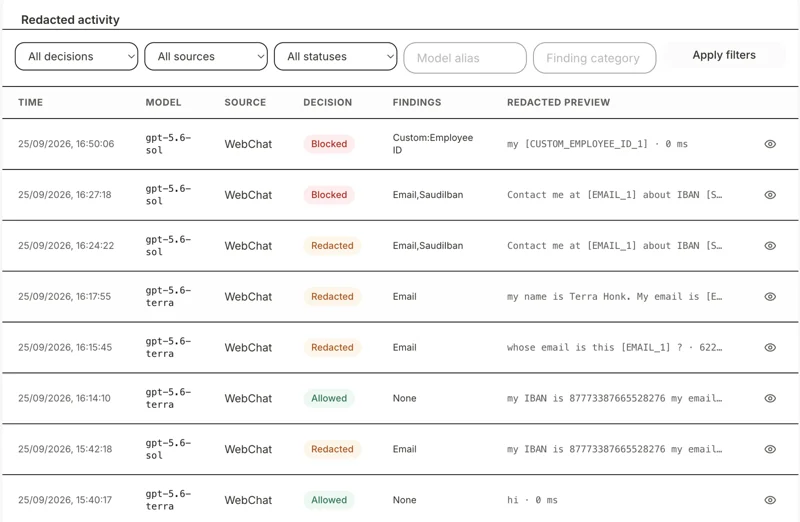
Illustrative example · synthetic data
A Saudi National ID is detected in a prompt. Choose a policy action to see how the request changes.
Employee prompt
Summarize this onboarding note. National ID: 1000000008.
Detected category: Saudi National ID
Model receives
Summarize this onboarding note. National ID: [SAUDINATIONALID_1].
The identifier is replaced before the request is forwarded.
This is a walkthrough, not a live scan. Actual detection and enforcement depend on your configured policy. Contextual Arabic and English personal-data detection uses your Azure AI Language resource.
See Arabic inspection and audit examplesInside the gateway
Follow a request from Saudi data detection and policy enforcement to an approved customer-owned model and privacy-safe audit evidence—inside your environment.
Control plane
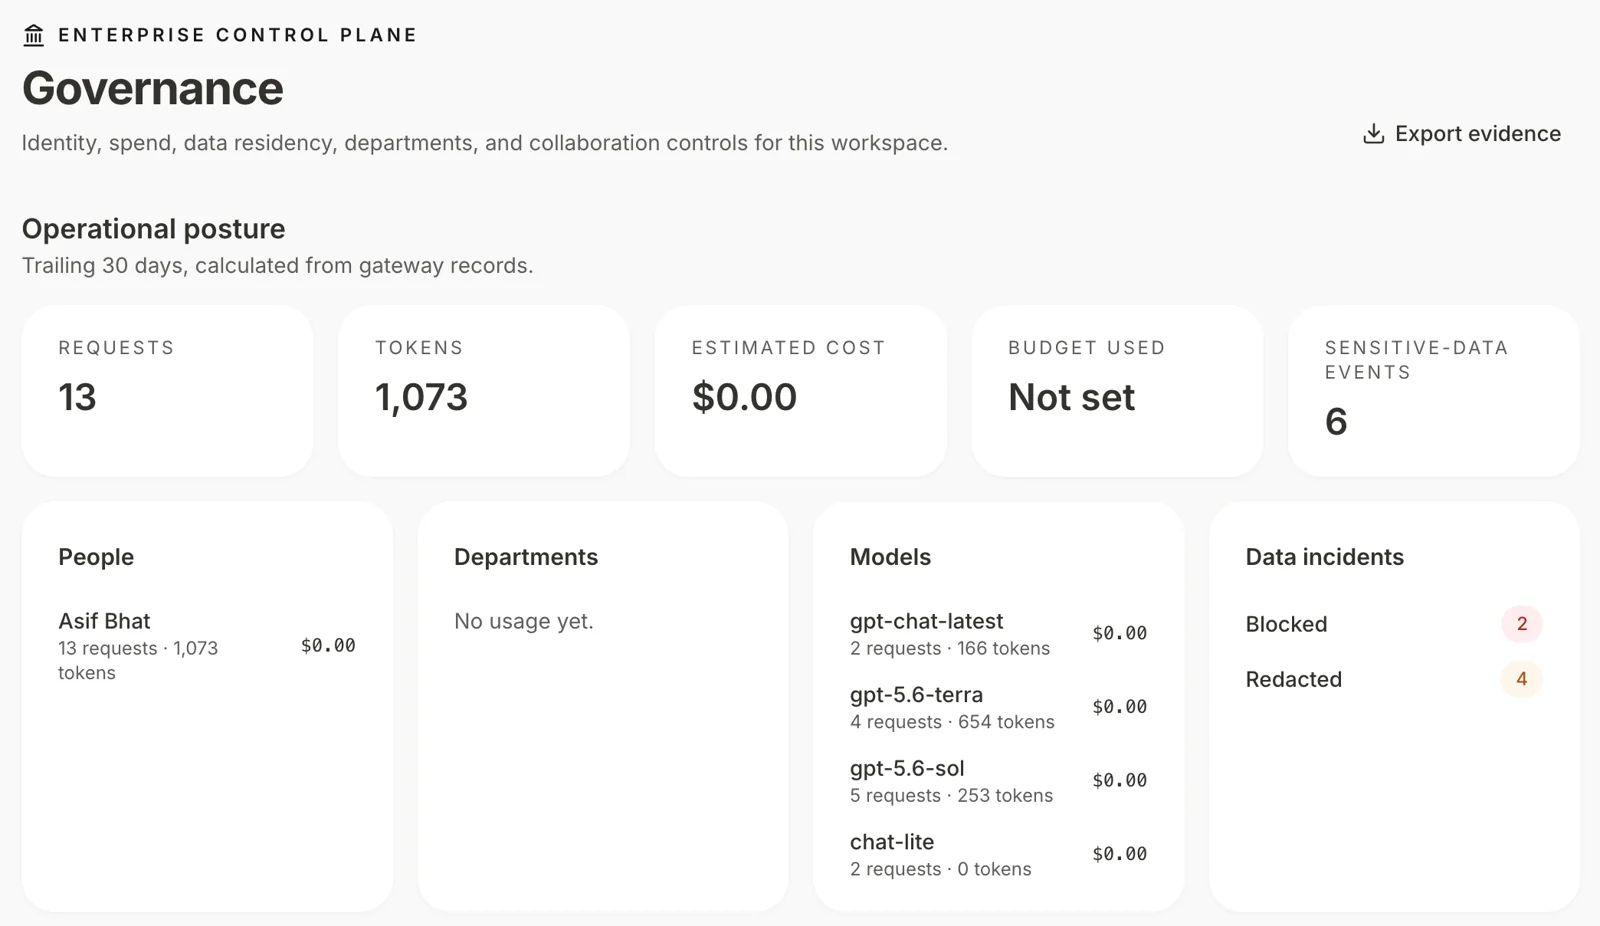
Give tenant administrators a live view of adoption, model usage, estimated cost, budgets, and sensitive-data events across the organization.
Operational outcome
One operational view
Policy, without the guesswork
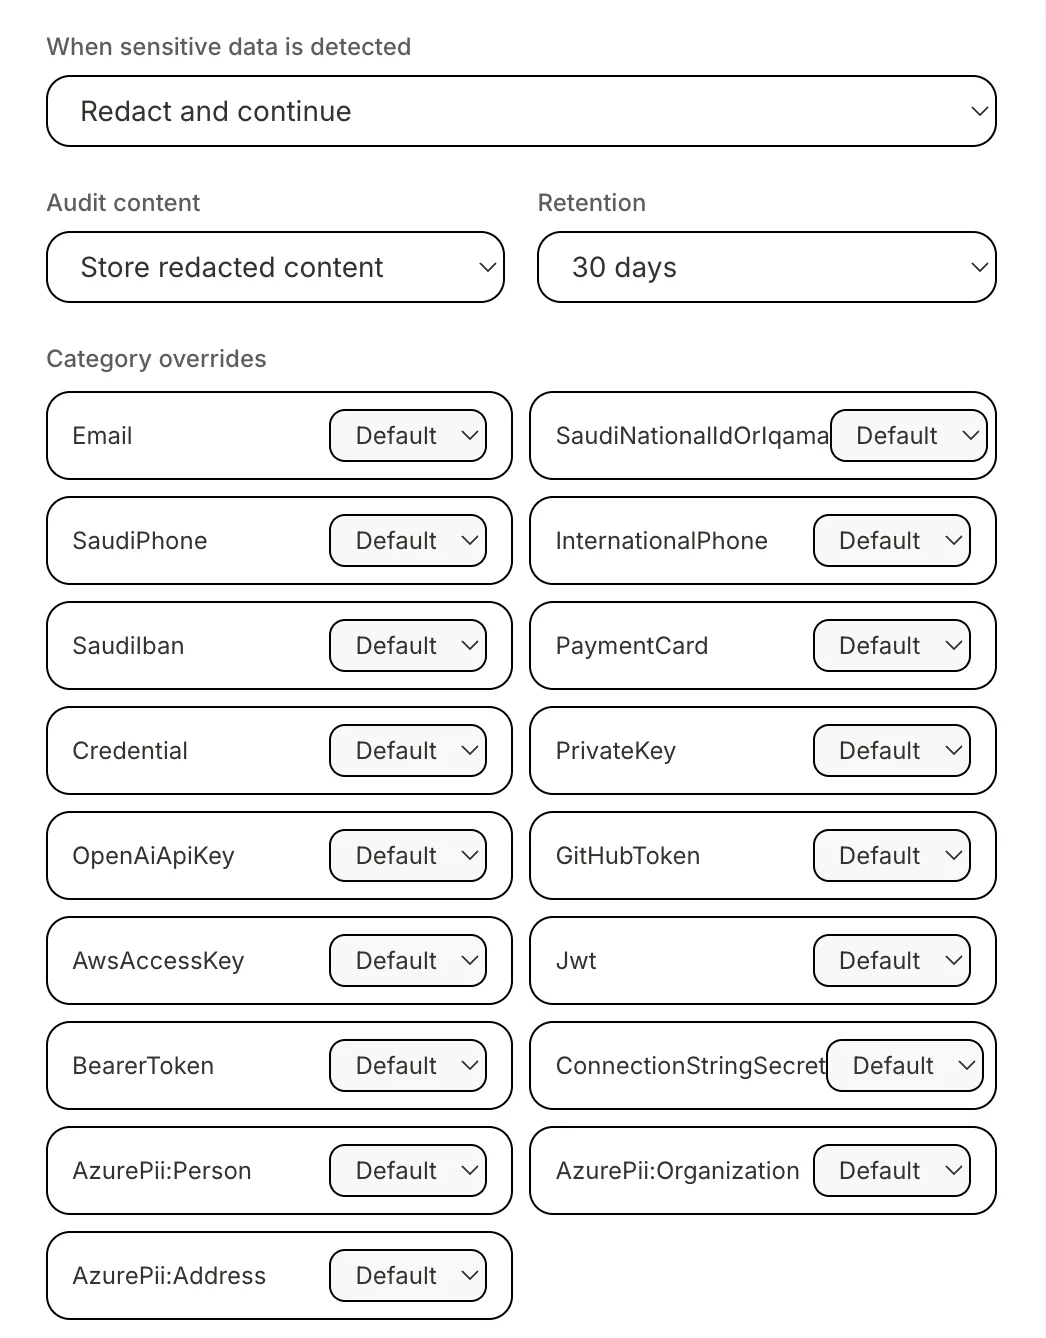
Start with built-in protection, tailor the action by category, and add company-specific identifiers without asking every administrator to write regular expressions.
01
Apply a default response and retain only the evidence your policy permits.
02
Protect validated Saudi identifiers, local number formats, credentials, tokens, and configured Arabic PII.
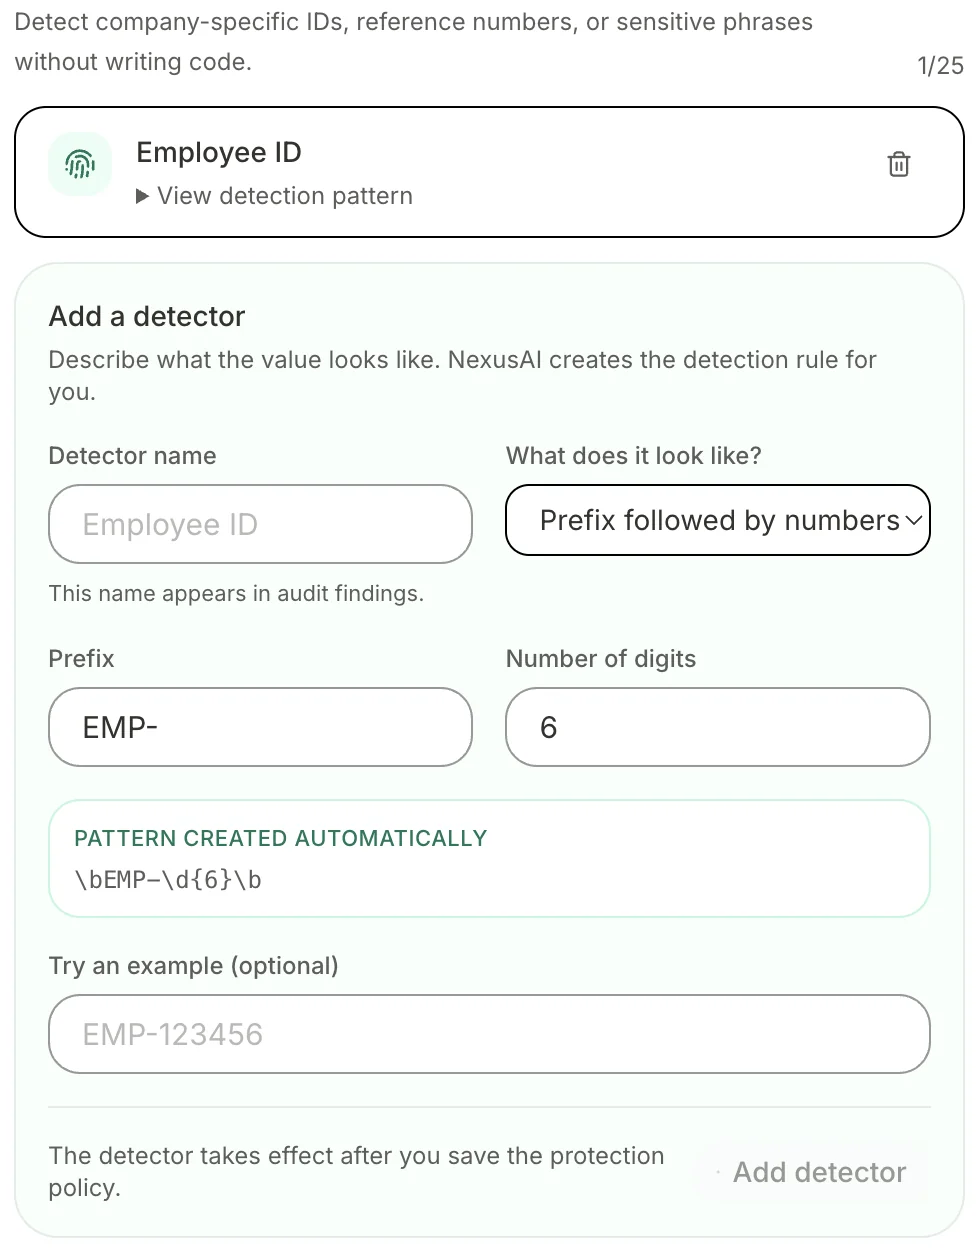
03
Describe an internal identifier and let the interface create the detection pattern.
The Saudi Data Protection Engine
Accepire recognizes Saudi formats in Western, Arabic-Indic, and Eastern Arabic digits. It validates IDs and IBANs, checks context around commercial registrations and Hijri dates, and can add Arabic and English personal-data detection through your configured Azure AI Language resource.
Customer administrators choose what is logged: metadata only, redacted prompt content, or no prompt-audit retention.
Validate Saudi formats locally in the gateway before a provider request is sent.
Reduce false positives for commercial registrations and Hijri dates with surrounding labels.
Use your Azure AI Language resource for configured Arabic and English entities.
The exposure happens first
An employee can paste an Iqama, Saudi IBAN, mobile number, credential, or Arabic personal information into an AI tool in seconds. Accepire puts detection and policy enforcement in the request path, before an approved model receives the prompt.
01
Shared credentials and disconnected tools make access difficult to review or revoke.
02
Prompts can contain local identifiers and Arabic personal information before anyone notices.
03
Usage, model cost, policy decisions, and audit records sit across separate systems.
Protect, then govern
Detect validated Saudi National IDs, Iqamas, IBANs, mobile numbers, labelled commercial registrations, contextual Hijri dates, credentials, and configured Arabic PII before a request reaches the model.
Connect Microsoft Entra ID and SCIM, map roles and groups, and remove access when people leave or change responsibilities.
Set approved models, Azure regions, budgets, request limits, and data-handling rules from one control plane.
Attribute requests, tokens, and estimated model cost by person, department, model, and channel without reselling model usage.
The ownership model
Accepire AI Gateway runs as a dedicated deployment in your Azure environment. You bring the cloud and approved models. We provide the governed access layer and help you put it into production.
You provide
Accepire provides
You get
You license the compiled software and receive deployment assistance, updates, and support. Your production workspace is not pooled with other customers, and you do not need to hand provider credentials to a shared Accepire service.
One policy, multiple channels
The same identity, model, budget, and data-protection rules follow every request—whether it starts in chat, Teams, a coding agent, or an internal application.
A governed workspace for employees
AI inside an existing work channel
OpenAI-compatible access for approved agents
A consistent API for internal products
From evaluation to production
01
We map your Azure environment, identity model, residency requirements, use cases, and security controls.
02
Accepire AI Gateway is deployed for a defined group with approved models, policies, and measurable acceptance criteria.
03
Add departments, channels, and models while retaining centralized policy, cost visibility, and evidence.
Accepire AI Gateway supports technical controls and evidence collection. Compliance depends on your complete architecture, configuration, operating procedures, and legal assessment.
See the protection flow
We’ll demonstrate detection, redaction, blocking, and audit evidence, then map the gateway to your Azure architecture, approved models, identity requirements, and pilot scope. Please do not bring real sensitive data to the public demo.